Multi-Cloud Hospitality Platform — AWS CloudFormation + Azure Front Door
Built a multi-cloud platform in two halves. On AWS, two CloudFormation stacks provision a public-services VPC (internet-facing ALB, Auto Scaling web tier in private subnets, bastion host) and a private-services VPC (RDS MySQL primary plus read replica, management instance), joined by VPC peering and deployed end to end by a GitHub Actions workflow. On Azure, a CLI script stores an FFmpeg-encoded adaptive-bitrate HLS stream in a private Blob container and serves it through Azure Front Door using a read-only SAS token.
- Problem
- App, data and admin tiers had to be isolated and deployed by pipeline, with HD video kept off the web servers.
- Services & tools
- CloudFormationGitHub ActionsVPC peeringALBRDSAzure Front Door
- Result
- Two peered VPCs deployed in one pipeline run; HLS video served from Azure's edge at ~91 ms per segment.
Architecture
- Step 1: A GitHub Actions run deploys the network stack, then the app stack that imports its outputs.
- Step 2: Guests reach the internet-facing ALB on 80/443.
- Step 3: The ALB forwards to the auto-scaled web tier in private subnets across two AZs.
- Step 4: Web servers reach RDS on 3306 across VPC peering. Security groups chain by reference; everything else is denied.
- Step 5: RDS MySQL is encrypted, backed up for seven days and has a read replica.
- Step 6: The management instance gets SSH/ICMP for diagnostics only.
- Step 7: Video is encoded into an adaptive HLS ladder and uploaded to a private Blob container.
- Step 8: Players request segments with a read-only, HTTPS-only SAS token via Front Door.
- Step 9: Front Door caches from the Blob origin, so video never loads the web tier (~91 ms TTFB per segment).
- Peered and segmented web and data tiers
- 2 VPCs
- ALB, Auto Scaling and RDS read replica
- 2 AZs
- Observed time to first byte per HLS segment
- ~91 ms
Why it matters
Keeps the booking application and customer data in a segmented, highly available AWS environment while moving heavy HD video to Azure's edge. Infrastructure rebuilds from code in one pipeline run, and video bandwidth no longer competes with the web tier.
The problem in detail
The scenario called for a hospitality platform whose application tier, database and management services are separated for security, deployed entirely by automation rather than console clicks, and paired with HD video tours that should not load the application servers. That meant designing network segmentation across two VPCs, getting stacks to deploy reliably in dependency order from a clean CI runner, and delivering private video content globally without making the storage public.
What I built
- 01
Split the infrastructure into two CloudFormation stacks: a network stack (VPCs, subnets, peering, route tables, security groups) whose outputs are exported, and an application stack that imports them, so networking can change without redeploying compute.
- 02
Designed VPC A (10.0.0.0/16) with public subnets for the ALB and NAT Gateway and private subnets for the web Auto Scaling group across two Availability Zones, and VPC B (10.1.0.0/16) with private subnets only — no internet gateway — for RDS and the management instance.
- 03
Created a VPC peering connection with routes in every route table, then chained security groups by reference: internet to ALB on 80/443, ALB to web servers on 80, web servers to RDS on 3306, and SSH/ICMP from the management instance for diagnostics. Everything else is denied.
- 04
Deployed RDS MySQL with encryption, seven-day backups, snapshot-on-delete and a read replica; launch template user data writes connection details from a CloudFormation parameter and a PHP page reports whether the primary and replica are reachable.
- 05
Built a workflow_dispatch GitHub Actions pipeline that loads AWS credentials and the database password from repository secrets and runs aws cloudformation deploy for each stack in order, printing the stack outputs at the end.
- 06
Encoded the demo video with FFmpeg into a 720p/1080p HLS ladder, uploaded it with the Azure CLI to a Blob container with anonymous access disabled, and configured Azure Front Door with the storage account as an HTTPS-only origin and caching for playlists and segments.
- 07
Played the stream with Shaka Player using a request filter that appends a read-only, HTTPS-only SAS to every segment request, then compared it with progressive MP4 delivery in the browser's network tools.
Evidence
01 / 12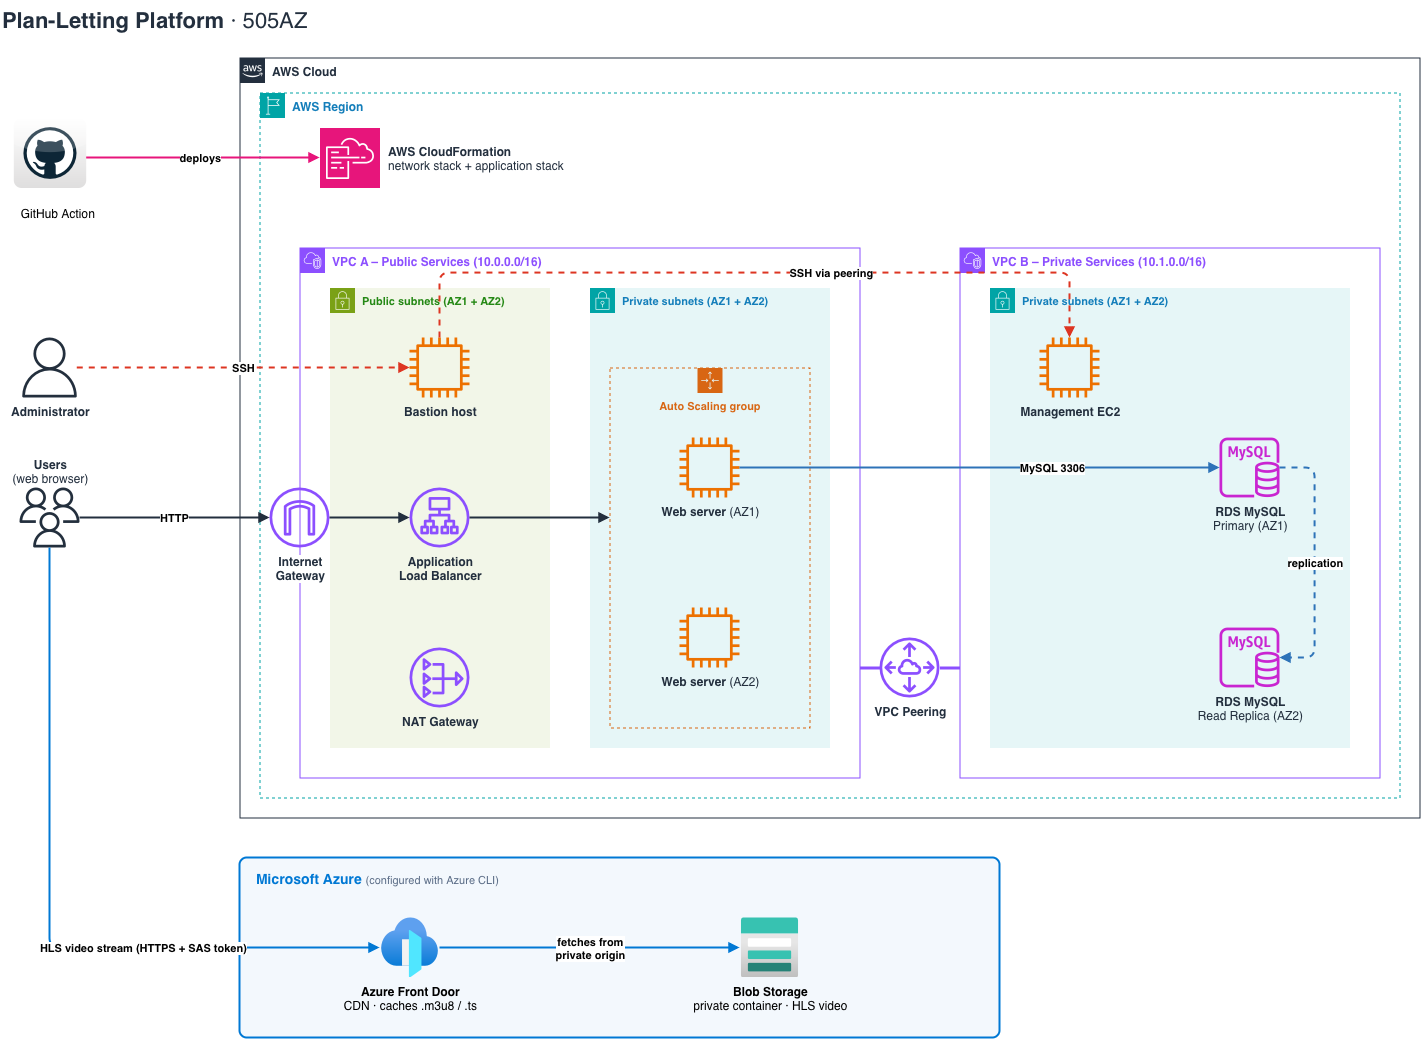
Architecture — GitHub Actions deploys two CloudFormation stacks: VPC A (ALB, Auto Scaling web tier, bastion, NAT) peered with VPC B (management EC2, RDS MySQL primary and read replica), while HD video streams over HTTPS from Azure Front Door and a private Blob container.