Enterprise Network — TechBridge
For an academic enterprise scenario, I designed, built and tested a full two-site network for the fictional TechBridge organisation — a London headquarters, Birmingham branch and public site — using a two-tier collapsed core with HSRP gateways, 22 VLANs, VLSM addressing sized for 50% growth, OSPF dynamic routing, NAT/PAT, ACL-filtered DMZs and a GRE-over-IPSec site-to-site tunnel, then validated every design decision with 18 documented tests.
- Problem
- Two sites needed room for 50% growth, no single point of failure and a private link between them.
- Tools
- Cisco IOSOSPFHSRPVLANsGRE/IPSecNAT/PAT
- Result
- 22 VLANs, HSRP failover and an encrypted site-to-site tunnel, validated by 18 end-to-end tests.
Architecture
- Step 1: Each department sits on its own VLAN; DHCP relay hands out addresses and the HSRP gateway.
- Step 2: Access switches trunk to an HSRP pair. If the active core fails, the standby takes over.
- Step 3: The core routes to the edge router; OSPF learns routes dynamically.
- Step 4: Inter-site traffic runs through a GRE tunnel protected by IPSec, never in clear over the internet.
- Step 5: NAT/PAT shares one public IP; ACLs allow only HTTP and ICMP into each DMZ.
- Step 6: Birmingham mirrors the design: OSPF, HSRP core pair and VLAN access layer.
- Growth headroom designed in
- 50%
- VLANs across both sites
- 22
- Tests passed end to end
- 18
Why it matters
Removes single points of failure, fragmented addressing and unencrypted inter-site traffic for a growing two-site business. The design absorbs 50% headcount growth without re-addressing and passed 18 end-to-end validation tests.
The problem in detail
The academic brief modelled a secure off-site data storage and recovery business whose London and Birmingham infrastructure could not meet its reliability, scalability, flexibility or security requirements. The network had to support roughly 500 hosts per department in London and 200 in Birmingham while absorbing 50% growth over two years without a redesign, keep departmental traffic isolated, survive the loss of a core switch without downtime, expose public-facing servers safely, and connect both sites privately rather than across the open internet.
What I built
- 01
Chose a two-tier collapsed core (core and distribution combined into layer 3 switches) to cut latency, simplify management and match the scale of a medium-sized organisation, with redundant core switches at each site.
- 02
Configured HSRP across the core switches so every VLAN has a single virtual gateway IP with an automatic standby, removing the core switch as a single point of failure.
- 03
Sized the addressing with VLSM: Class C 192.168.x.x /22 in London (1,022 usable hosts per VLAN against a 750-host requirement) and Class B 172.16.x.x /23 in Birmingham (510 hosts against 300 required), with /30 links for every WAN transit hop to avoid wasting addresses.
- 04
Segmented London into 8 departmental VLANs plus a DMZ and management VLAN, and Birmingham into 10 VLANs plus DMZ and management, keeping broadcast domains small and departments logically isolated.
- 05
Ran OSPF internally and externally for dynamic route discovery and redundant paths, backed by static default routes on the WAN routers pointing to each ISP (PlusNET for London, O2 for Birmingham).
- 06
Built a GRE tunnel protected by IPSec VPN policies between the two sites, so inter-site traffic is encrypted and separated from the public internet.
- 07
Centralised addressing with DHCP servers per site and DHCP relay (IP helper) on the layer 3 switches, so every VLAN leases addresses, masks and HSRP gateways automatically.
- 08
Applied NAT/PAT overload on the edge routers so thousands of internal devices share a single public IP, and ACLs (including ACL 190) to permit only HTTP and ICMP into the DMZ servers.
- 09
Hardened device access with SSH-only management, MOTD banners and a dedicated management VLAN; secured wireless with WPA2-PSK/AES and per-VLAN SSIDs on non-overlapping channels 1, 6 and 11.
- 10
Selected and justified hardware: 2811 routers at the WAN edge for NAT, OSPF and IPSec; 3650-24PS layer 3 switches as the collapsed core for inter-VLAN routing, HSRP and relay; 2960 access switches for VLAN tagging and redundant trunks.
- 11
Validated the build with 18 tests covering SSH access, site-to-site reachability, end-to-end PC traffic, HSRP failover state, DHCP leases, NAT translations, STP convergence, inter-VLAN routing, wireless association, IP helper behaviour, OSPF tables and IPSec security associations before and after traffic.
Evidence
01 / 30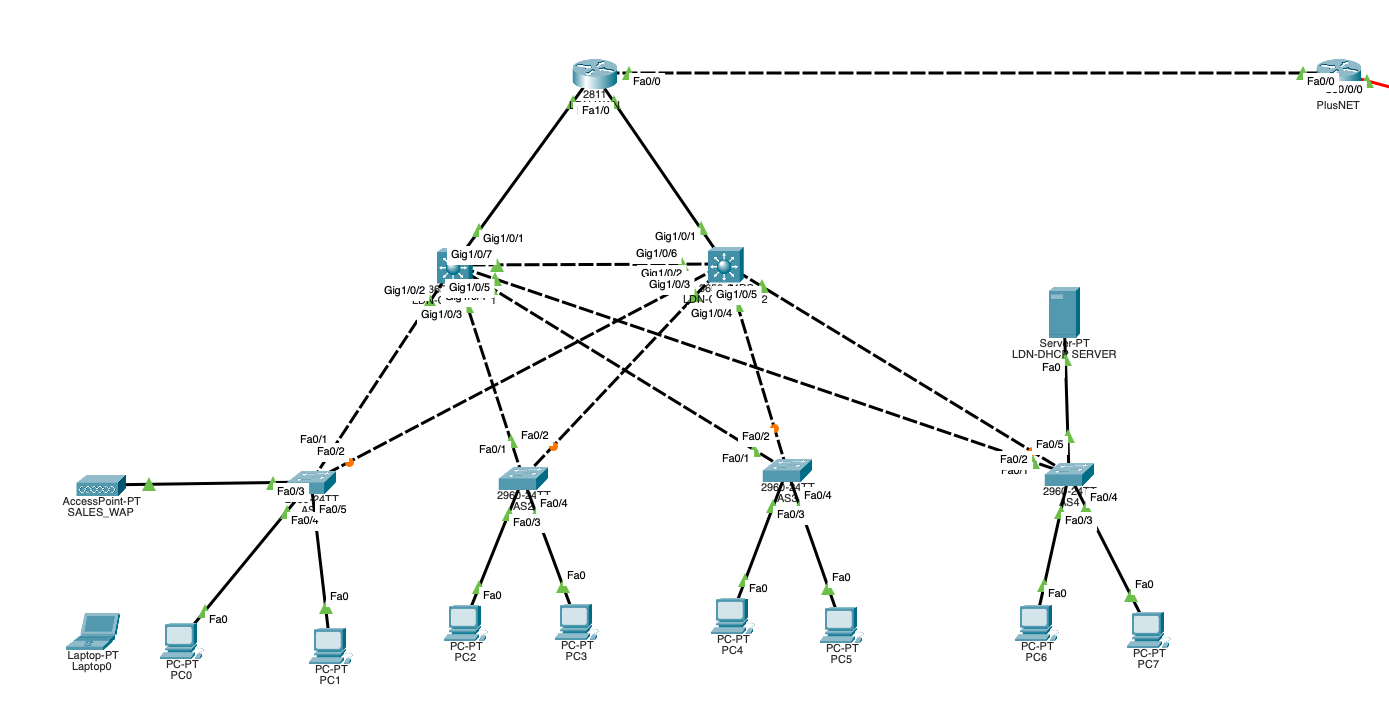
Headquarters architecture — two-tier collapsed core in London, with redundant layer 3 core switches running HSRP for a single resilient gateway.