Starling Digital Cloud Migration
Engineered a highly available, secure, decoupled multi-tier AWS environment for a cloud migration, aligned with the AWS Well-Architected Framework.
- Problem
- A fintech brief: move to AWS in a way that is secure, highly available and ready for audit.
- AWS services
- VPCALBEC2 Auto ScalingRDSDynamoDBEFSS3Simple AD
- Result
- Multi-AZ design, a 2–4 instance auto-scaled API tier, central identity and four chained security groups.
Architecture
- Step 1: Users reach the VPC through the internet gateway over HTTPS.
- Step 2: The Application Load Balancer in the public subnets takes the request.
- Step 3: It forwards to the Node.js API tier, auto-scaled 2–4 instances across both AZs.
- Step 4: The API reads and writes RDS; the DB security group only accepts the backend.
- Step 5: Market data is stored in DynamoDB.
- Step 6: User data mounts shared EFS storage when each instance boots.
- Step 7: Instances join the Starling.Digital domain in Simple AD through SSSD.
- Step 8: Admins SSH to the bastion host, then on to private instances. No direct SSH from the internet.
- High availability
- Multi-AZ
- Compliance posture
- Audit-ready
- API tier
- Auto-scaled
Why it matters
Moves a regulated digital-services team off manually managed single instances and onto a secure, scalable AWS operating model. Multi-AZ services and a 2–4 instance Auto Scaling range improve continuity, while central identity and reusable bootstrapping cut repeat configuration and access risk.
The problem in detail
I created the fictional Starling Digital brief to test how I would design a cloud migration that was secure, highly available, audit-ready and decoupled.
What I built
- 01
Built a Multi-AZ VPC with public/private subnet segregation and stateful security groups enforcing least privilege.
- 02
Integrated AWS Simple AD for centralised directory services, automated Linux RBAC and SSSD domain joining.
- 03
Deployed an Auto Scaling Node.js API tier behind an ALB, bootstrapped via User Data scripts handling DNS, EFS mounting and security config.
- 04
Provisioned Multi-AZ RDS subnets, DynamoDB for market data, shared EFS storage and versioned S3 buckets for compliance.
Evidence
01 / 18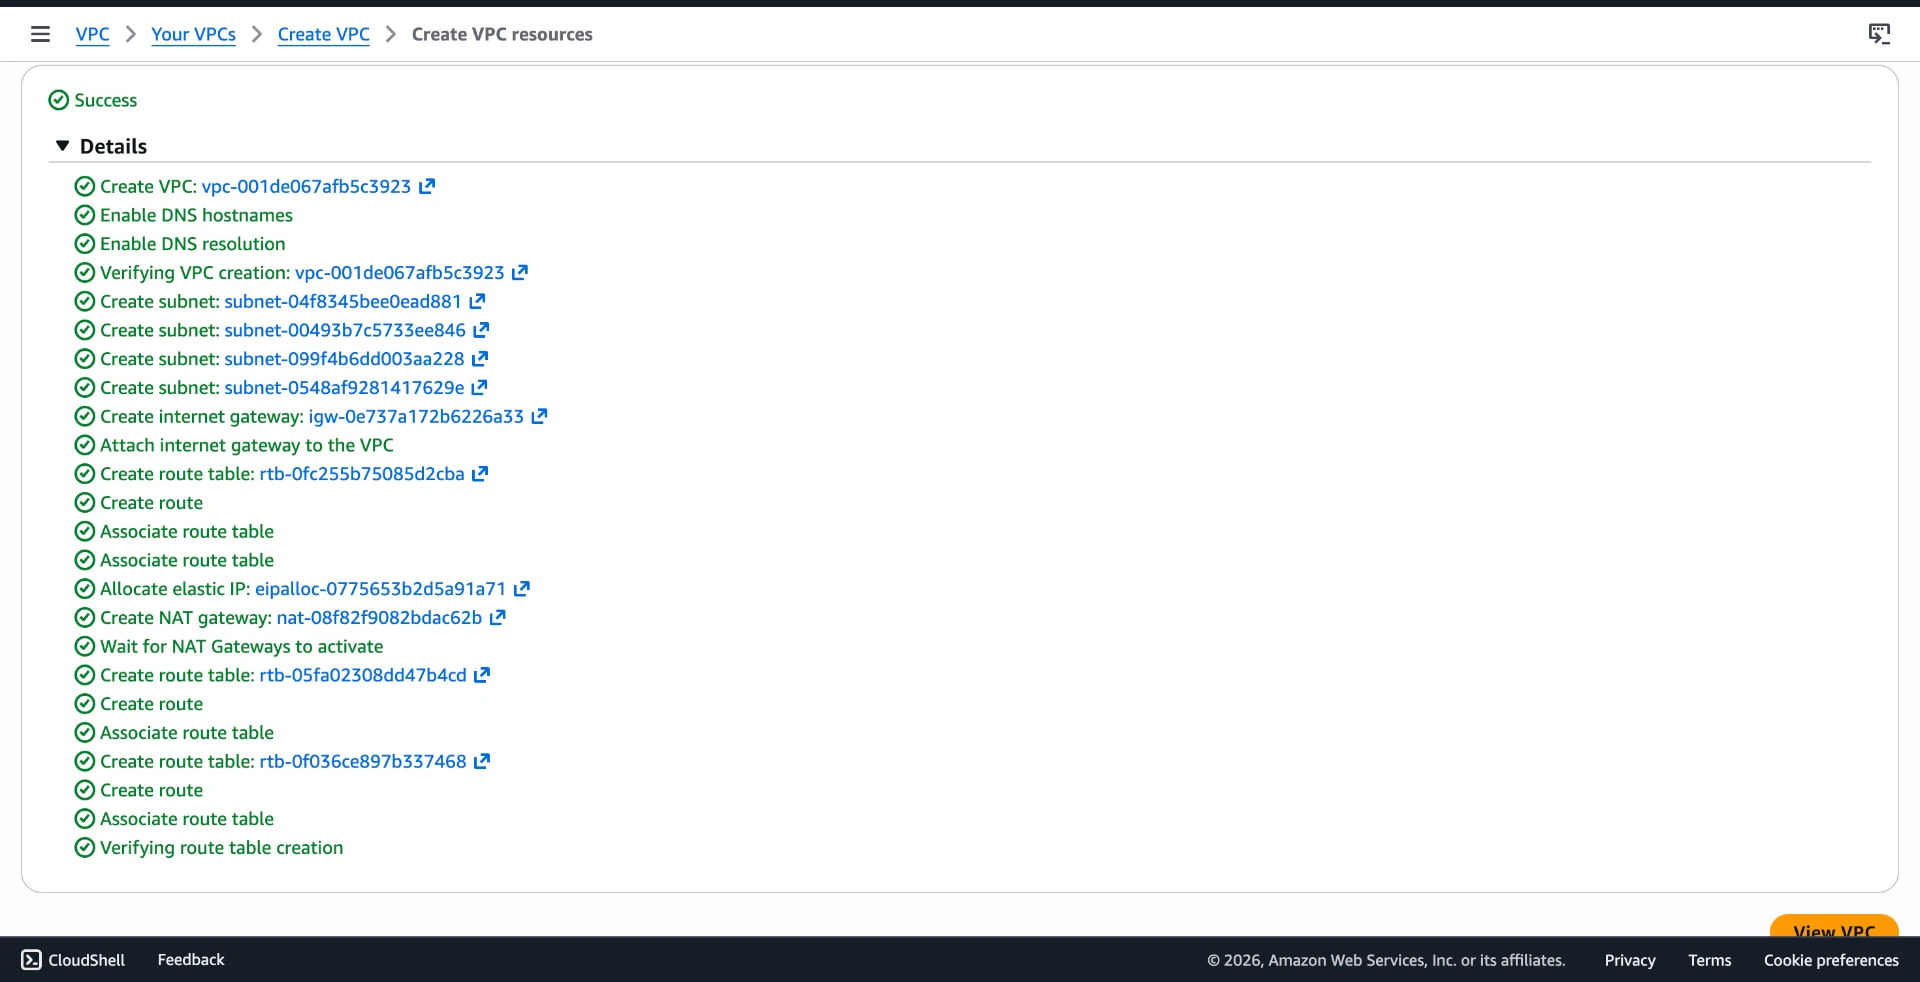
Stage 01 — VPC build-out: subnets, internet gateway, NAT gateway, route tables and associations all provisioned successfully.